HIPAA & Healthcare Security Compliance Statement
RMI BPO LLC d/b/a MediNexus Billing operates as a Business Associate to covered healthcare entities. This comprehensive statement outlines our multi-layered technical, administrative, and physical safeguards governing electronic Protected Health Information (ePHI).
Regulatory Status & Business Associate Role
RMI BPO LLC d/b/a MediNexus Billing ("MediNexus", "Company", "we", "us", or "our") provides revenue cycle management, certified medical coding, claim scrubbing, clearinghouse submission, denial management, credentialing, and accounts receivable recovery services to medical practices, physicians, hospitals, and ambulatory surgery centers (collectively, "Covered Entities").
In the performance of these administrative healthcare operations, MediNexus operates strictly as a Business Associate as defined under 45 C.F.R. § 160.103 of the Health Insurance Portability and Accountability Act of 1996 ("HIPAA"), the Health Information Technology for Economic and Clinical Health Act ("HITECH Act"), Title XIII of the American Recovery and Reinvestment Act of 2009 ("ARRA"), and the HIPAA Omnibus Final Rule of 2013.
Pursuant to Section 13401 of the HITECH Act and 45 C.F.R. § 164.308, MediNexus is directly liable under civil and criminal federal law to the United States Department of Health and Human Services (HHS) Office for Civil Rights (OCR) for full compliance with the HIPAA Security Rule and applicable sections of the Privacy Rule.
Scope of Protected Health Information (PHI)
In delivering revenue cycle operations, we handle Protected Health Information ("PHI") and electronic Protected Health Information ("ePHI") transmitted by Covered Entities or generated by our clearinghouse interfaces. This data encompasses, but is not limited to:
- Patient Identifiers: Legal names, residential addresses, dates of birth, Social Security Numbers, phone numbers, and emergency contact details.
- Clinical & Encounter Documentation: Progress notes, operative reports, diagnostic imaging interpretations, pathology summaries, and physician orders.
- Coding & Billing Records: ICD-10-CM diagnosis codes, CPT/HCPCS procedural codes, modifiers, charge entries, superbills, and encounter forms.
- Insurance & Payer Data: Commercial subscriber numbers, Medicare/Medicaid Beneficiary Identifiers (MBI), group plan IDs, copay/coinsurance data, prior authorization numbers, and coordination of benefits details.
- Financial & Remittance Records: Explanation of Benefits (EOB), Electronic Remittance Advice (ERA 835), patient billing statements, payment histories, and collection notes.
Administrative Safeguards (45 CFR § 164.308)
MediNexus has established formal, documented operational policies and administrative safeguards designed to manage the selection, development, implementation, and maintenance of security measures to protect ePHI:
3.1 Security Management Process (§ 164.308(a)(1))
We conduct continuous, documented risk analyses to assess potential vulnerabilities to the confidentiality, integrity, and availability of electronic health records. Our risk management program applies active countermeasures, automated vulnerability scanning, and third-party penetration testing.
3.2 Assigned Security Responsibility (§ 164.308(a)(2))
MediNexus has appointed an executive-level Chief Information Security Officer (CISO) and a designated HIPAA Privacy Officer endowed with full institutional authority to enforce compliance across all corporate systems, facilities, and personnel.
3.3 Workforce Security & Authorization (§ 164.308(a)(3))
All employees, contractors, and coding specialists undergo thorough pre-employment background screening, criminal background checks, and OIG/SAM exclusion list verifications. Access to billing systems is granted strictly based on role authorization and immediately revoked upon termination within 1 hour.
3.4 Contingency Planning & Disaster Recovery (§ 164.308(a)(7))
Our infrastructure maintains geo-redundant real-time database replication across Tier IV data centers located in separate US geographic zones. Daily encrypted snapshots ensure a Recovery Point Objective (RPO) of < 15 minutes and a Recovery Time Objective (RTO) of < 2 hours during catastrophic disaster scenarios.
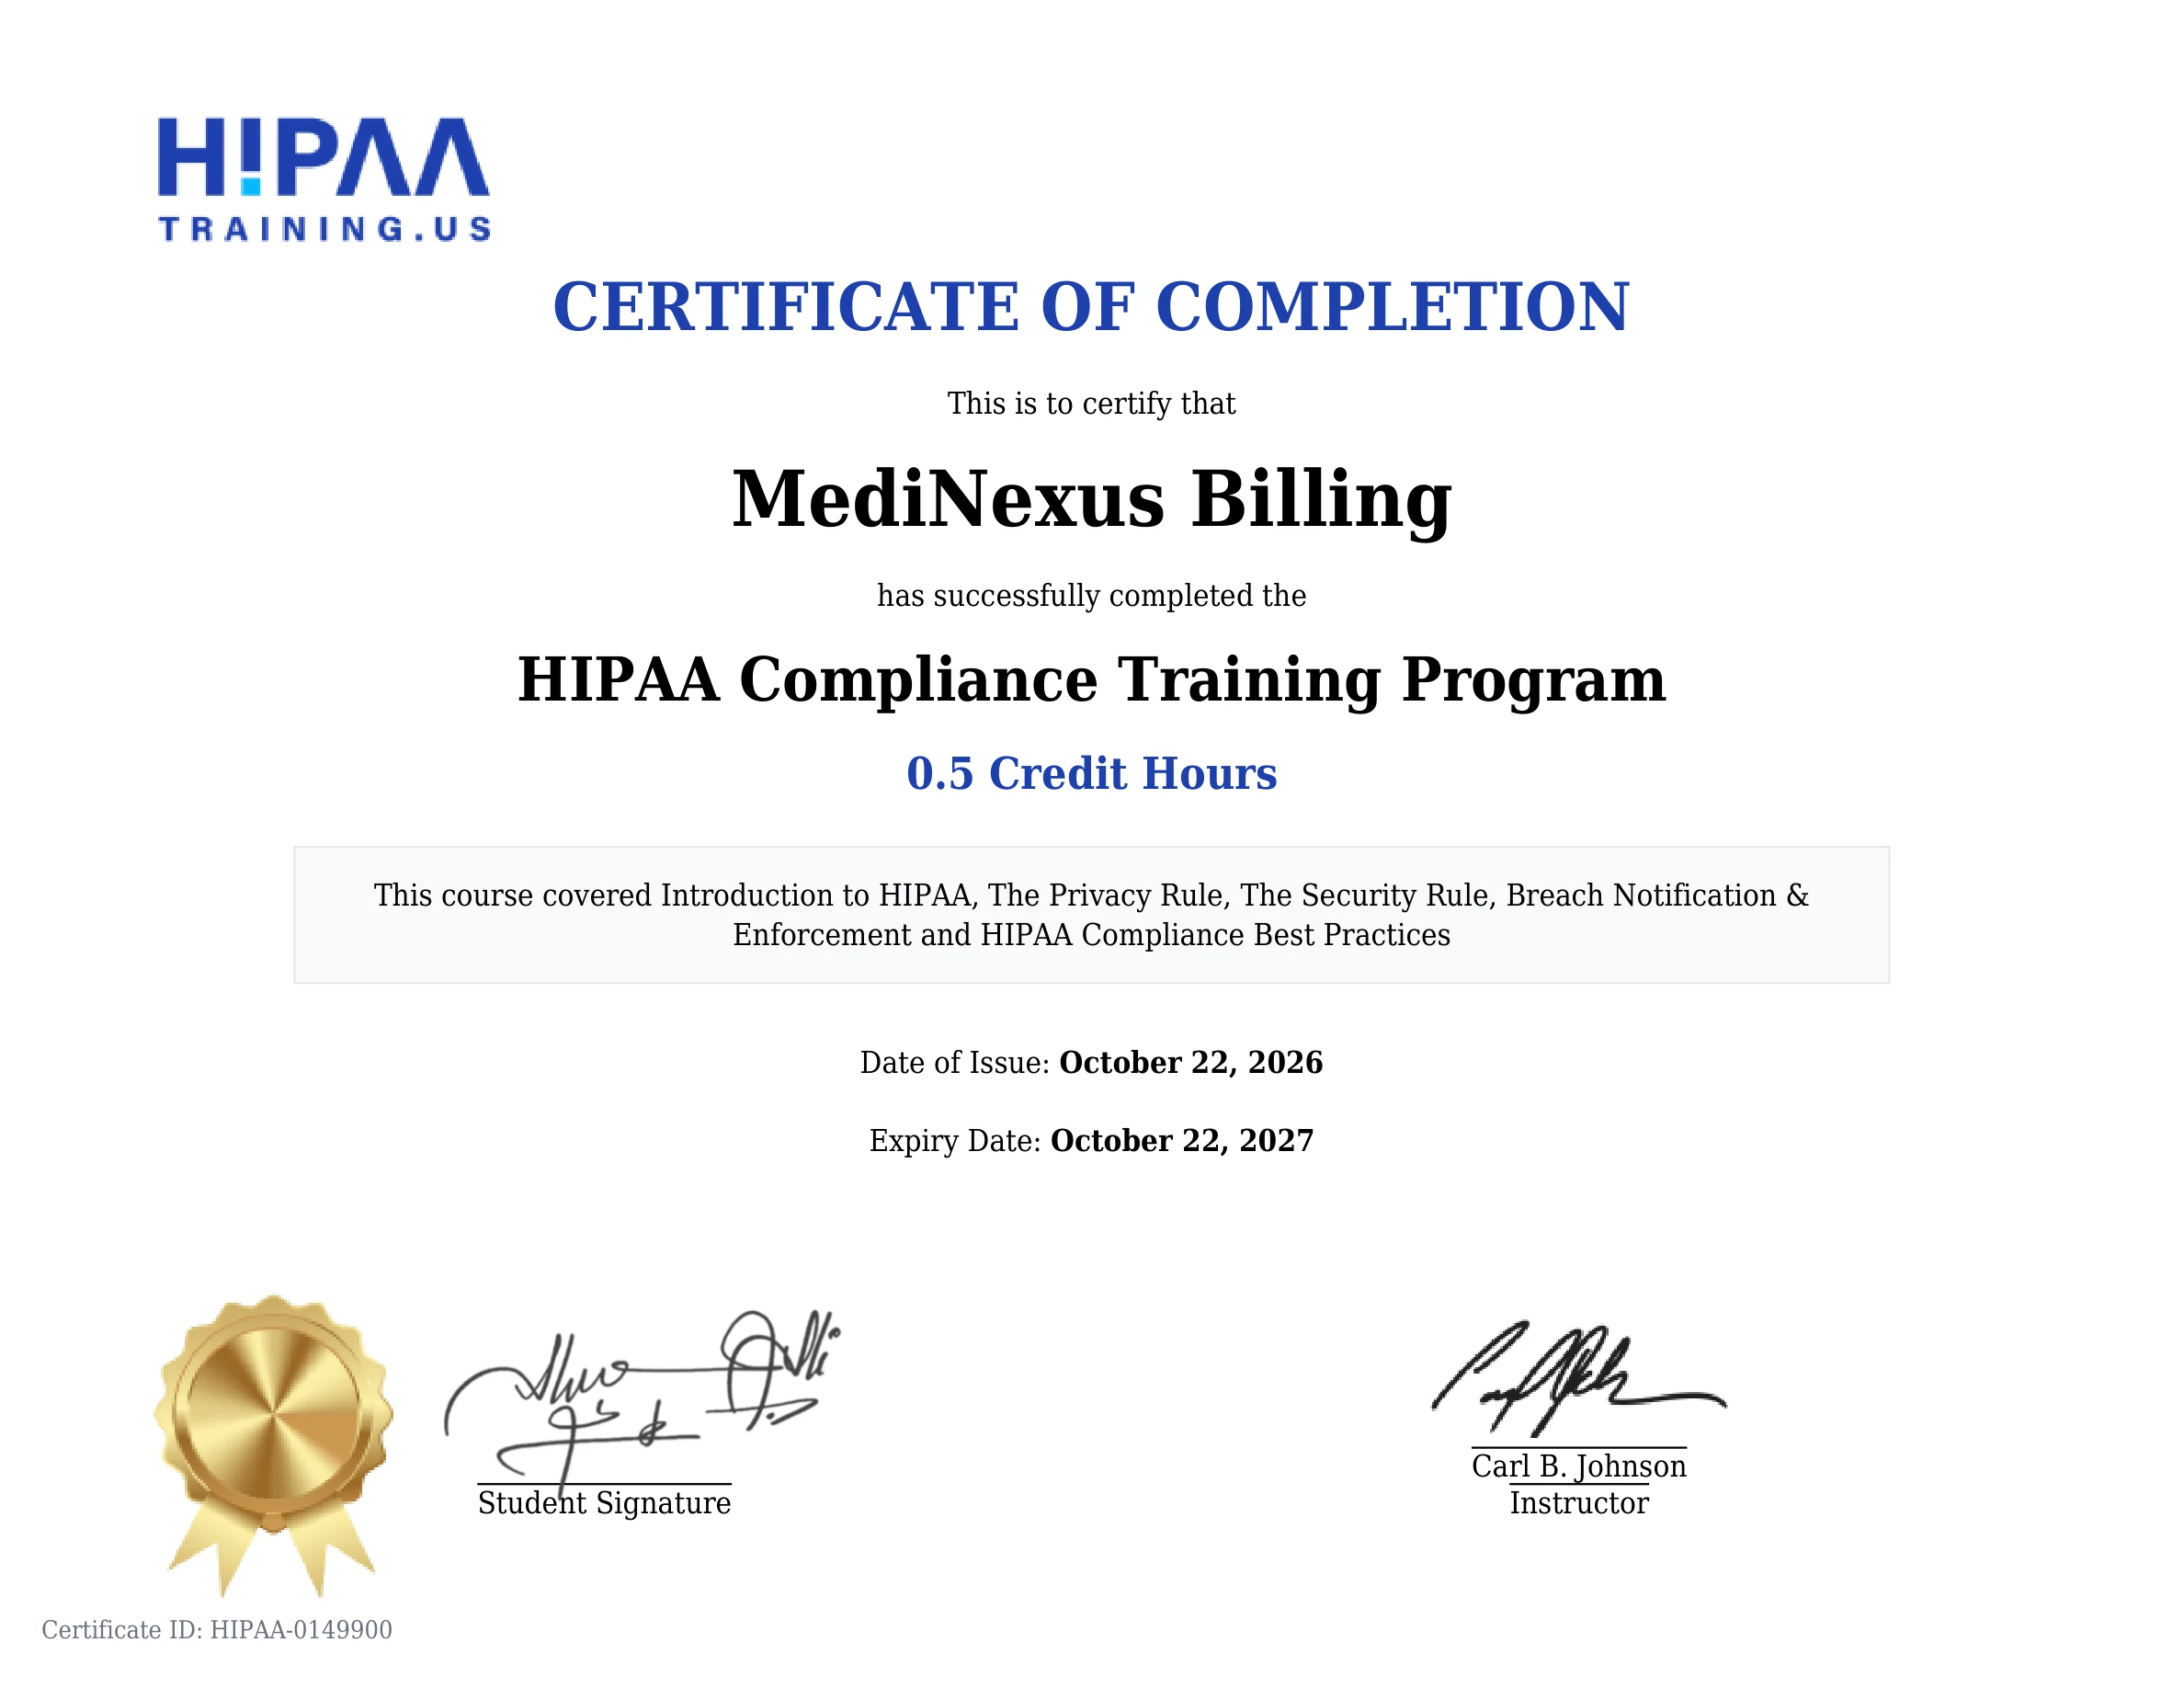
HIPAA Compliance Training Program Certification
Accredited by HIPAA Training.US under certified instructor Carl B. Johnson. Covers the HIPAA Privacy Rule, Security Rule, administrative & technical safeguards, breach notification, and healthcare compliance best practices.
Technical Safeguards & Cryptography (45 CFR § 164.312)
MediNexus applies state-of-the-art technological controls to prevent unauthorized electronic access to patient billing records:
Physical & Environmental Safeguards (45 CFR § 164.310)
MediNexus enforces strict physical boundaries protecting facilities, servers, and workstations:
- Biometric & Badge Access: Entry to billing operations floors requires biometric verification or dual-factor electronic RFID badges. All visitor entries are logged and escorted 100% of the time.
- Clean Desk Policy: Physical writing pads, personal cell phones, cameras, and unauthorized paper records are strictly forbidden on active billing and coding production floors.
- Hardware Port Lockdown: All computer workstations have physical and BIOS-level locks disabling USB storage, external hard drives, Bluetooth data transfer, and optical drives to eliminate localized exfiltration.
- Hardware Destruction: Decommissioned hard drives, servers, and media are destroyed on-site by National Association for Information Destruction (NAID) certified contractors providing serialized certificates of destruction.
Privacy Rule & Minimum Necessary Standard
In accordance with 45 C.F.R. § 164.502(b), MediNexus adheres strictly to the Minimum Necessary Rule. Our workforce members only access the specific portions of medical records required to perform the discrete billing, coding, or appeal function assigned:
For example, our payment posting teams have access to financial remittances, billing identifiers, and procedure codes, but do not have access to full psychiatric psychotherapy notes or sensitive clinical histories.
MediNexus does not use, sell, monetize, disclose, or de-identify patient health records for commercial data brokerage, pharmaceutical marketing, or artificial intelligence training without explicit statutory authorization.
Business Associate Agreement (BAA) Protocols
Prior to receiving, accessing, or transmitting any ePHI on behalf of a Covered Entity, MediNexus executes a legally binding, standardized Business Associate Agreement meeting all requirements of 45 C.F.R. § 164.504(e). Our standard BAA guarantees that MediNexus shall:
- Use or disclose ePHI solely as permitted or required by the Master Services Agreement or as required by federal/state law.
- Use appropriate administrative, physical, and technical safeguards to prevent use or disclosure of ePHI other than as provided for by the agreement.
- Mitigate, to the extent practicable, any harmful effect that is known to MediNexus of a use or disclosure of ePHI in violation of the requirements of the agreement.
- Report to the Covered Entity any security incident or breach of unsecured ePHI of which it becomes aware within statutory timeframes.
- Ensure that any subcontractors or agents that create, receive, maintain, or transmit ePHI on behalf of MediNexus agree to the same restrictions and conditions.
- Make available ePHI in accordance with 45 C.F.R. § 164.524 (Access of Individuals to PHI).
- Return or securely destroy all ePHI upon termination of the Master Services Agreement.
Incident Response & Breach Notification Protocol
MediNexus maintains an active, tested Computer Security Incident Response Plan (CSIRP) pursuant to 45 C.F.R. §§ 164.400–414 (Breach Notification Rule).
Any suspected unauthorized acquisition, access, use, or disclosure of unencrypted ePHI triggers an immediate forensic investigation assessing: (1) The nature and extent of the PHI involved, including types of identifiers; (2) The unauthorized person who used or received the PHI; (3) Whether the PHI was actually acquired or viewed; and (4) The extent to which risk has been mitigated.
Covered Entity Notification: MediNexus notifies affected Covered Entities without unreasonable delay and in no case later than twenty-four (24) to forty-eight (48) hours following discovery of a verified breach—well within the federal 60-day maximum statutory allowance—to enable timely regulatory filings with HHS OCR.
Downstream Vendor & Clearinghouse Governance
MediNexus routes electronic transactions exclusively through accredited, SOC 2 Type II certified electronic clearinghouses (e.g. Waystar, Availity, Change Healthcare). Every downstream vendor, clearinghouse gateway, cloud hosting provider, and archival repository executes written Downstream Business Associate Agreements binding them to the identical strict security covenants governing MediNexus.
Workforce Training & Sanctions Policy
Human vigilance is our first line of defense. All MediNexus staff undergo rigorous mandatory compliance training:
- Initial Hire Certification: Prior to being granted access to any client platform or live chart, employees must achieve 100% on comprehensive HIPAA Security and Privacy competency examinations.
- Continuous Phishing & Threat Testing: Automated simulated spear-phishing campaigns are run bi-weekly; employees failing simulations undergo immediate remedial training.
- Zero-Tolerance Sanction Policy: Intentional, unauthorized snooping, disclosure, or mishandling of patient health records results in immediate termination, forfeiture of credentials, and reporting to civil/criminal law enforcement.
Privacy & Security Officer Contact Information
To request an executed copy of our Business Associate Agreement, report a potential security incident, or inspect our third-party compliance audit summaries, please contact our Privacy Office: