Security Accreditations & Certifications
Healthcare providers trust MediNexus Billing with their most sensitive patient health information and clinical revenues. Review our active statutory certifications, PCI DSS merchant validations, and HIPAA training credentials below.
Certificate of PCI DSS Merchant Compliance
Payment Card Industry Data Security Standards (SAQ C-VT 3.2.1)
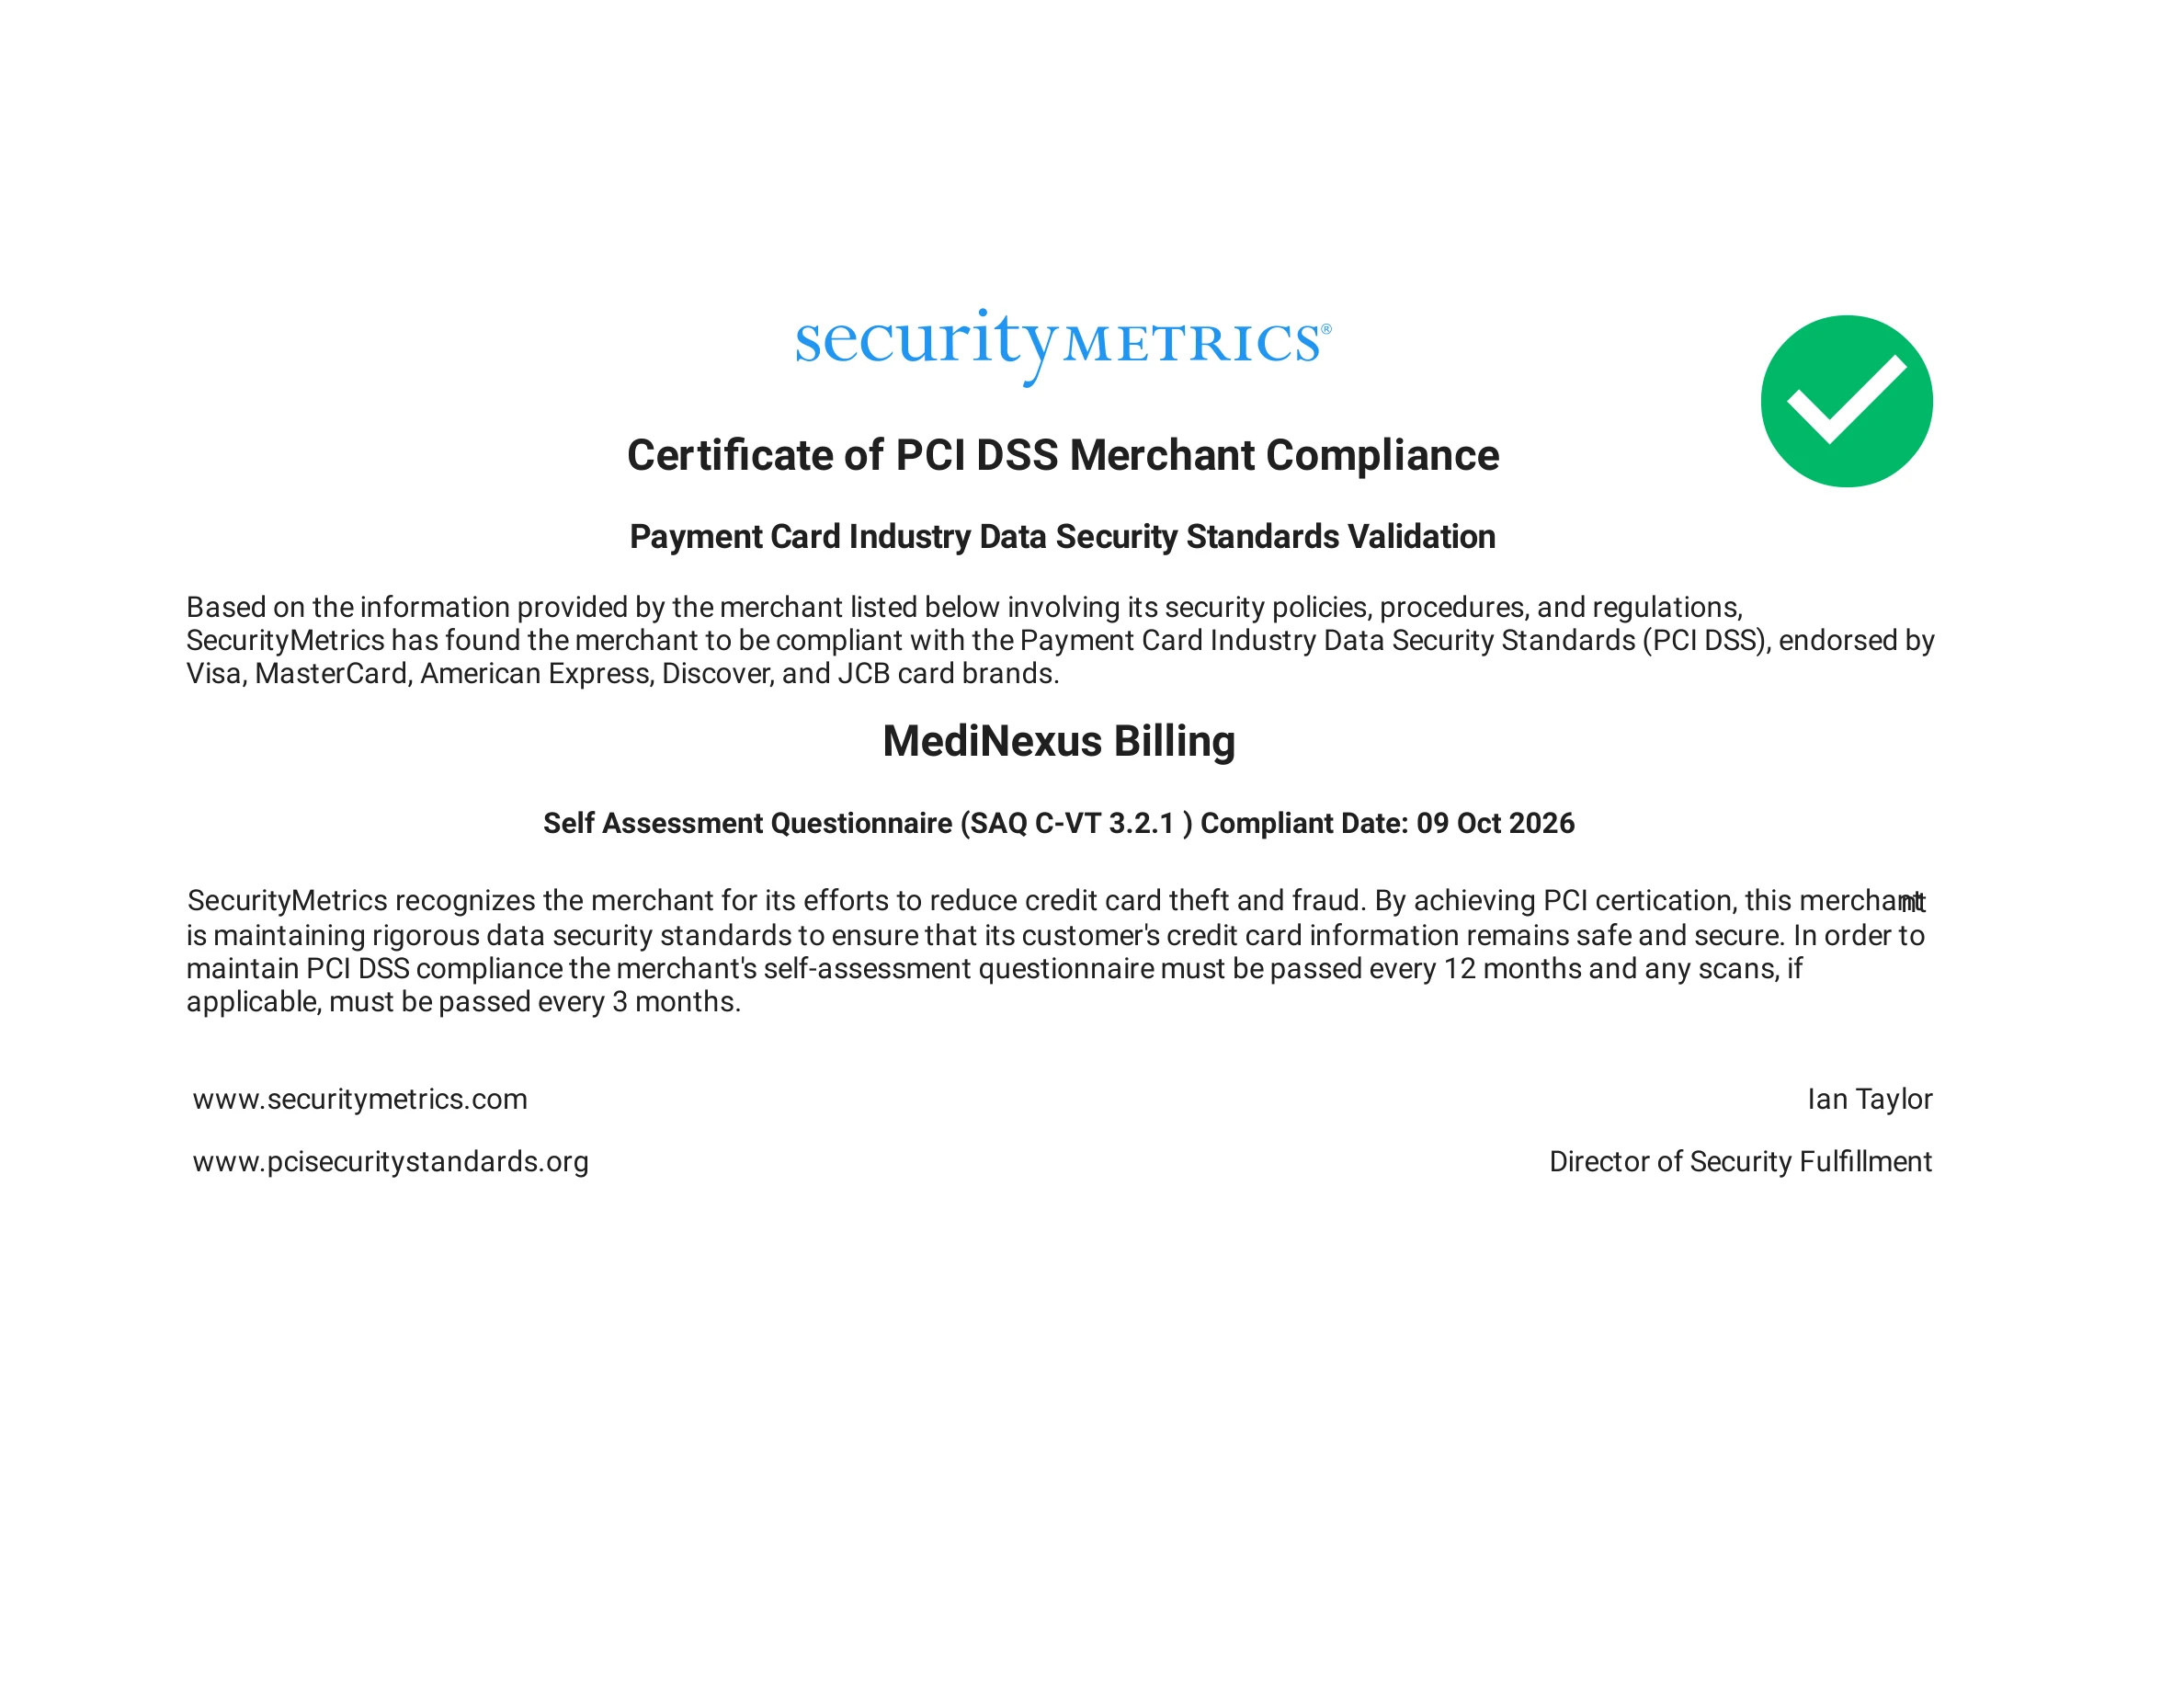
SecurityMetrics has validated MediNexus Billing's technical security policies, network controls, and payment card handling procedures against rigorous Payment Card Industry Data Security Standards (PCI DSS). Ensures patient credit card transactions and merchant processing remain strictly safe, encrypted, and fraud-resistant.
HIPAA Compliance Training & Certification
HIPAA Privacy Rule, Security Rule & Breach Notification (45 CFR)
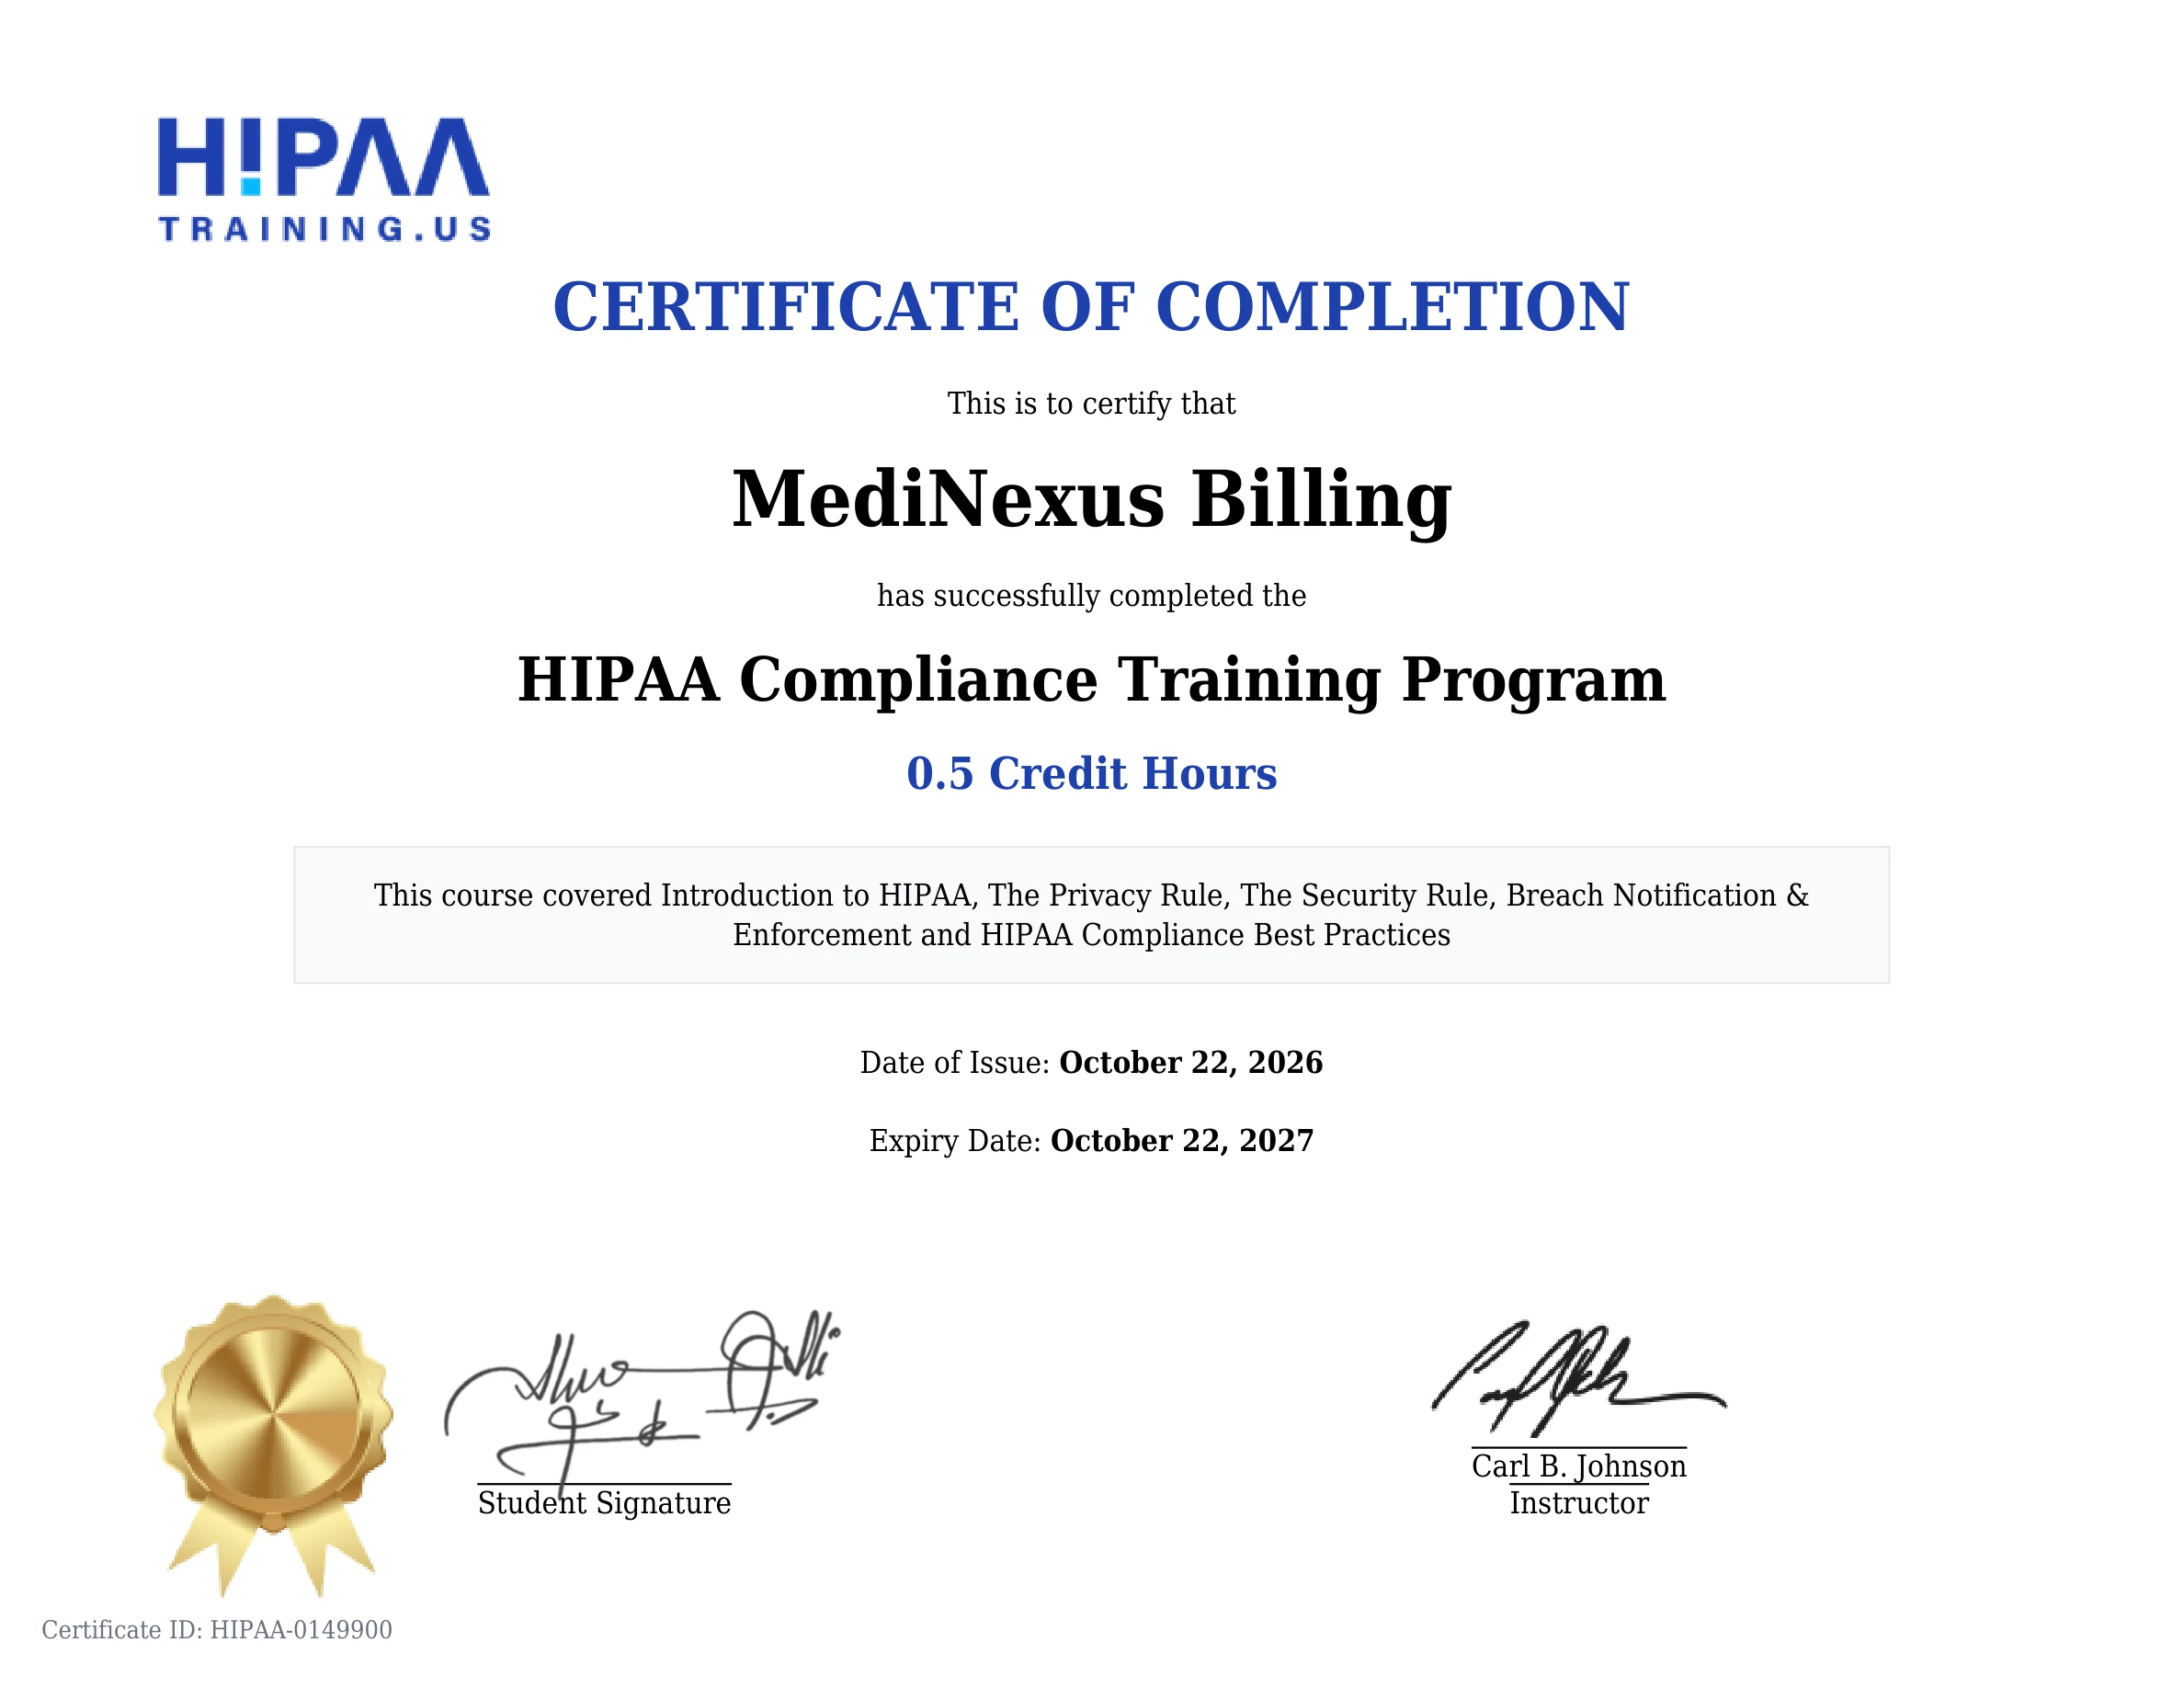
Validates completion of comprehensive healthcare compliance covering the HIPAA Privacy Rule, Security Rule, administrative & technical safeguards, breach notification protocols, and healthcare cybersecurity best practices for protected health information (ePHI).
Our 4 Pillars of Healthcare Data Protection
Compliance is not a one-time badge—it is an active, continuous operational discipline embedded across every pod, workstation, and clearinghouse batch.
PCI DSS Validation
Certified under SAQ C-VT 3.2.1 by SecurityMetrics. Protects patient co-pays, credit card data, and online portal billing under Visa/Mastercard/Amex standards.
HIPAA & HITECH Act
Comprehensive workforce training under 45 CFR Parts 160 & 164. Strict adherence to the Privacy Rule, Security Rule, and Minimum Necessary Standard.
256-Bit Cryptography
End-to-end TLS 1.3 encryption in transit and AES-256 encryption at rest. Continuous audit logs tracking all electronic claim files and remits.
Executed BAA Standard
Every medical clinic, provider group, and health system is protected by an executed HIPAA Business Associate Agreement signed under RMI BPO LLC.